The Qodex blog
Articles and guides on API testing, QA automation, and CI.
What Is API Testing? Types, Examples & Best Practices
Learn API testing from first request to CI. See test types, a runnable example, automation, tools, best practices, and a checklist for reliable APIs.
Read the article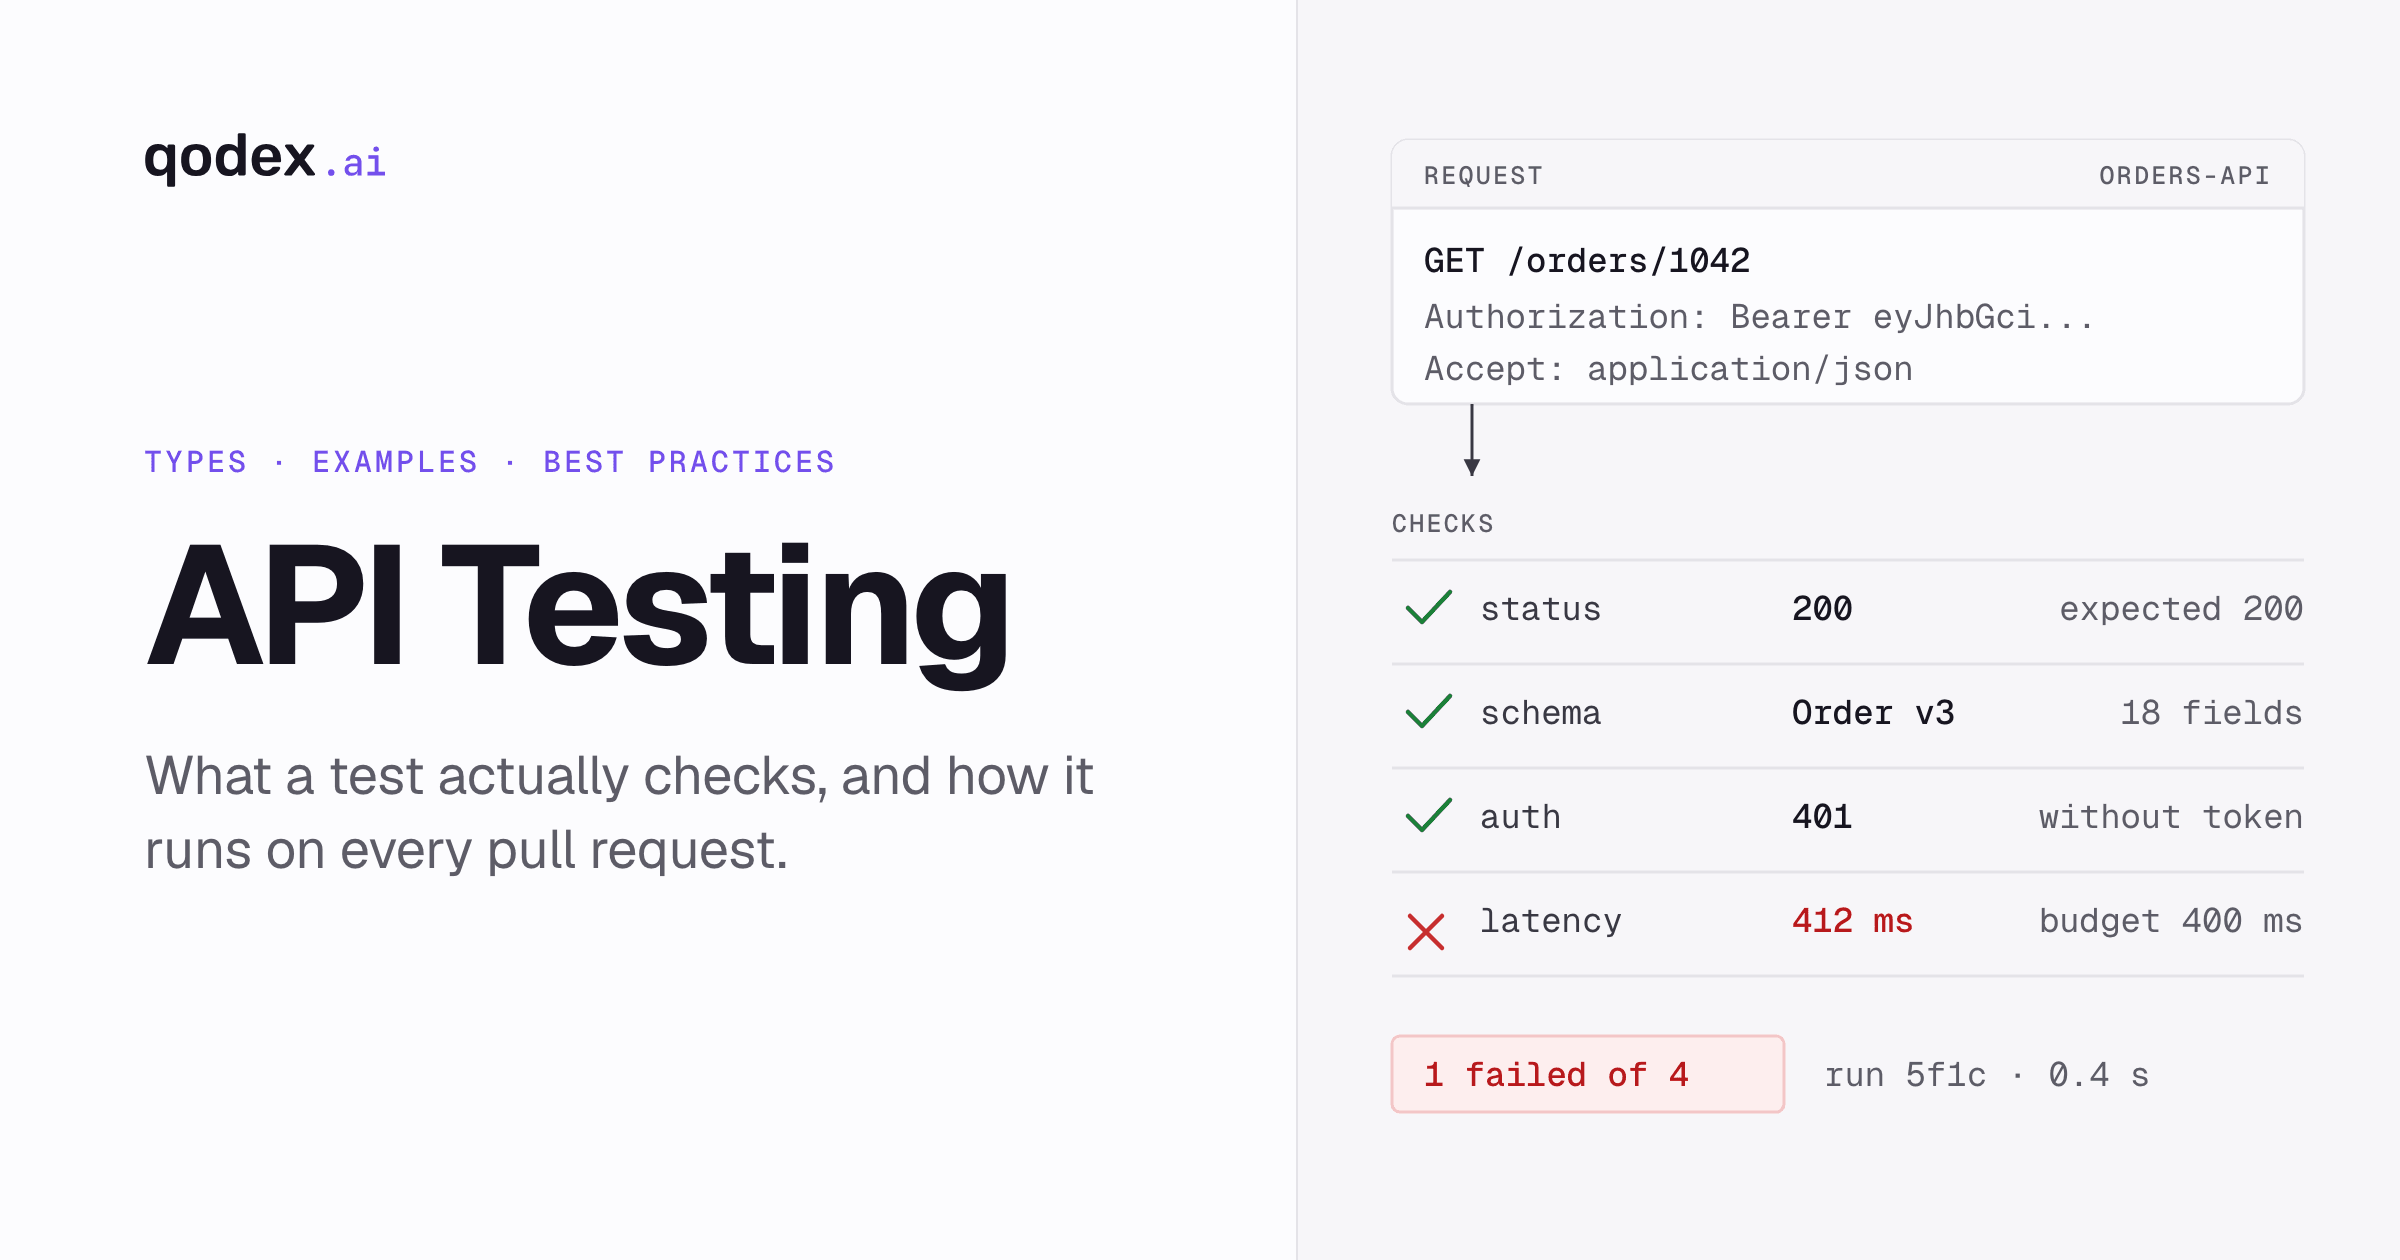
All articles
Security Testing Tools and its Types
Essential security testing tools and their types, including SAST, DAST, and IAST, to protect your software from vulnerabilities.
API Security Best Practices for 2026: Gateway/WAAP, OAuth 2.1, Workload Identity & CI/CD Recipes
Protect your APIs with 15 proven security practices: authentication, rate limiting, input validation, encryption, and real-time monitoring.
SQL Injection (SQLi): Types, Examples & Prevention
Understand all SQL injection types with real examples. Prevent SQLi using parameterized queries, WAF rules, and a step-by-step detection playbook.
API Inventory: Why You Need One & 10 Steps to Build It
Build a complete API inventory in 10 steps. Reduce shadow API risk, improve security posture, and stay compliant with this actionable guide.
Broken Function-Level Authorization: Prevention
What is broken function level authorization (BFLA)? Learn how this OWASP API vulnerability works, real-world examples, and how to prevent it.
10 LLM Security Tools
Essential security tools designed to protect Large Language Models from vulnerabilities like prompt injection and data leaks.
API Attacks: Real-World Examples, OWASP Risks & Prevention
Most common API attacks, real-world breach examples, OWASP Top 10 risks, and practical defenses to secure APIs end-to-end.
12 Best API Vulnerability Scanner Tools in 2026
Compare 12 API vulnerability scanners by scope, authentication, evidence, false-positive handling, CI/CD fit, pricing, and hands-on use.
IAST vs DAST: Key Differences & How to Choose
IAST vs DAST compared: accuracy, CI/CD fit, false positives, and setup complexity. Use our decision framework to pick the right AppSec approach.
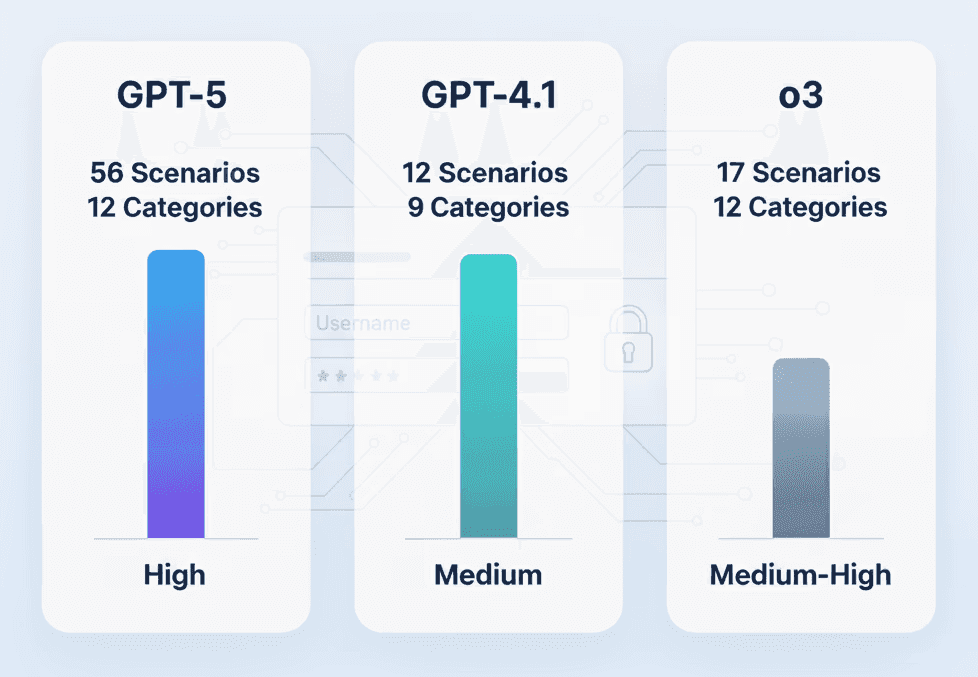
GPT-5 vs O3 vs GPT-4.1 for Penetration Testing
We tested GPT-5, O3, and GPT-4.1 on real pen testing tasks. See which AI model finds more vulnerabilities and produces actionable reports.
What Is Burp Suite, and 10 Burp Suite Alternatives and Competitors
Top Burp Suite alternatives for web security testing, Caido, OWASP ZAP, StackHawk, and more. Compare features, pricing, and CI/CD integration.
What Is OAuth 2.0 and How Does It Work?
OAuth 2.0 fundamentals: secure authorization framework, token-based access, and API security best practices for developers in 2026.