12 Best API Vulnerability Scanner Tools in 2026
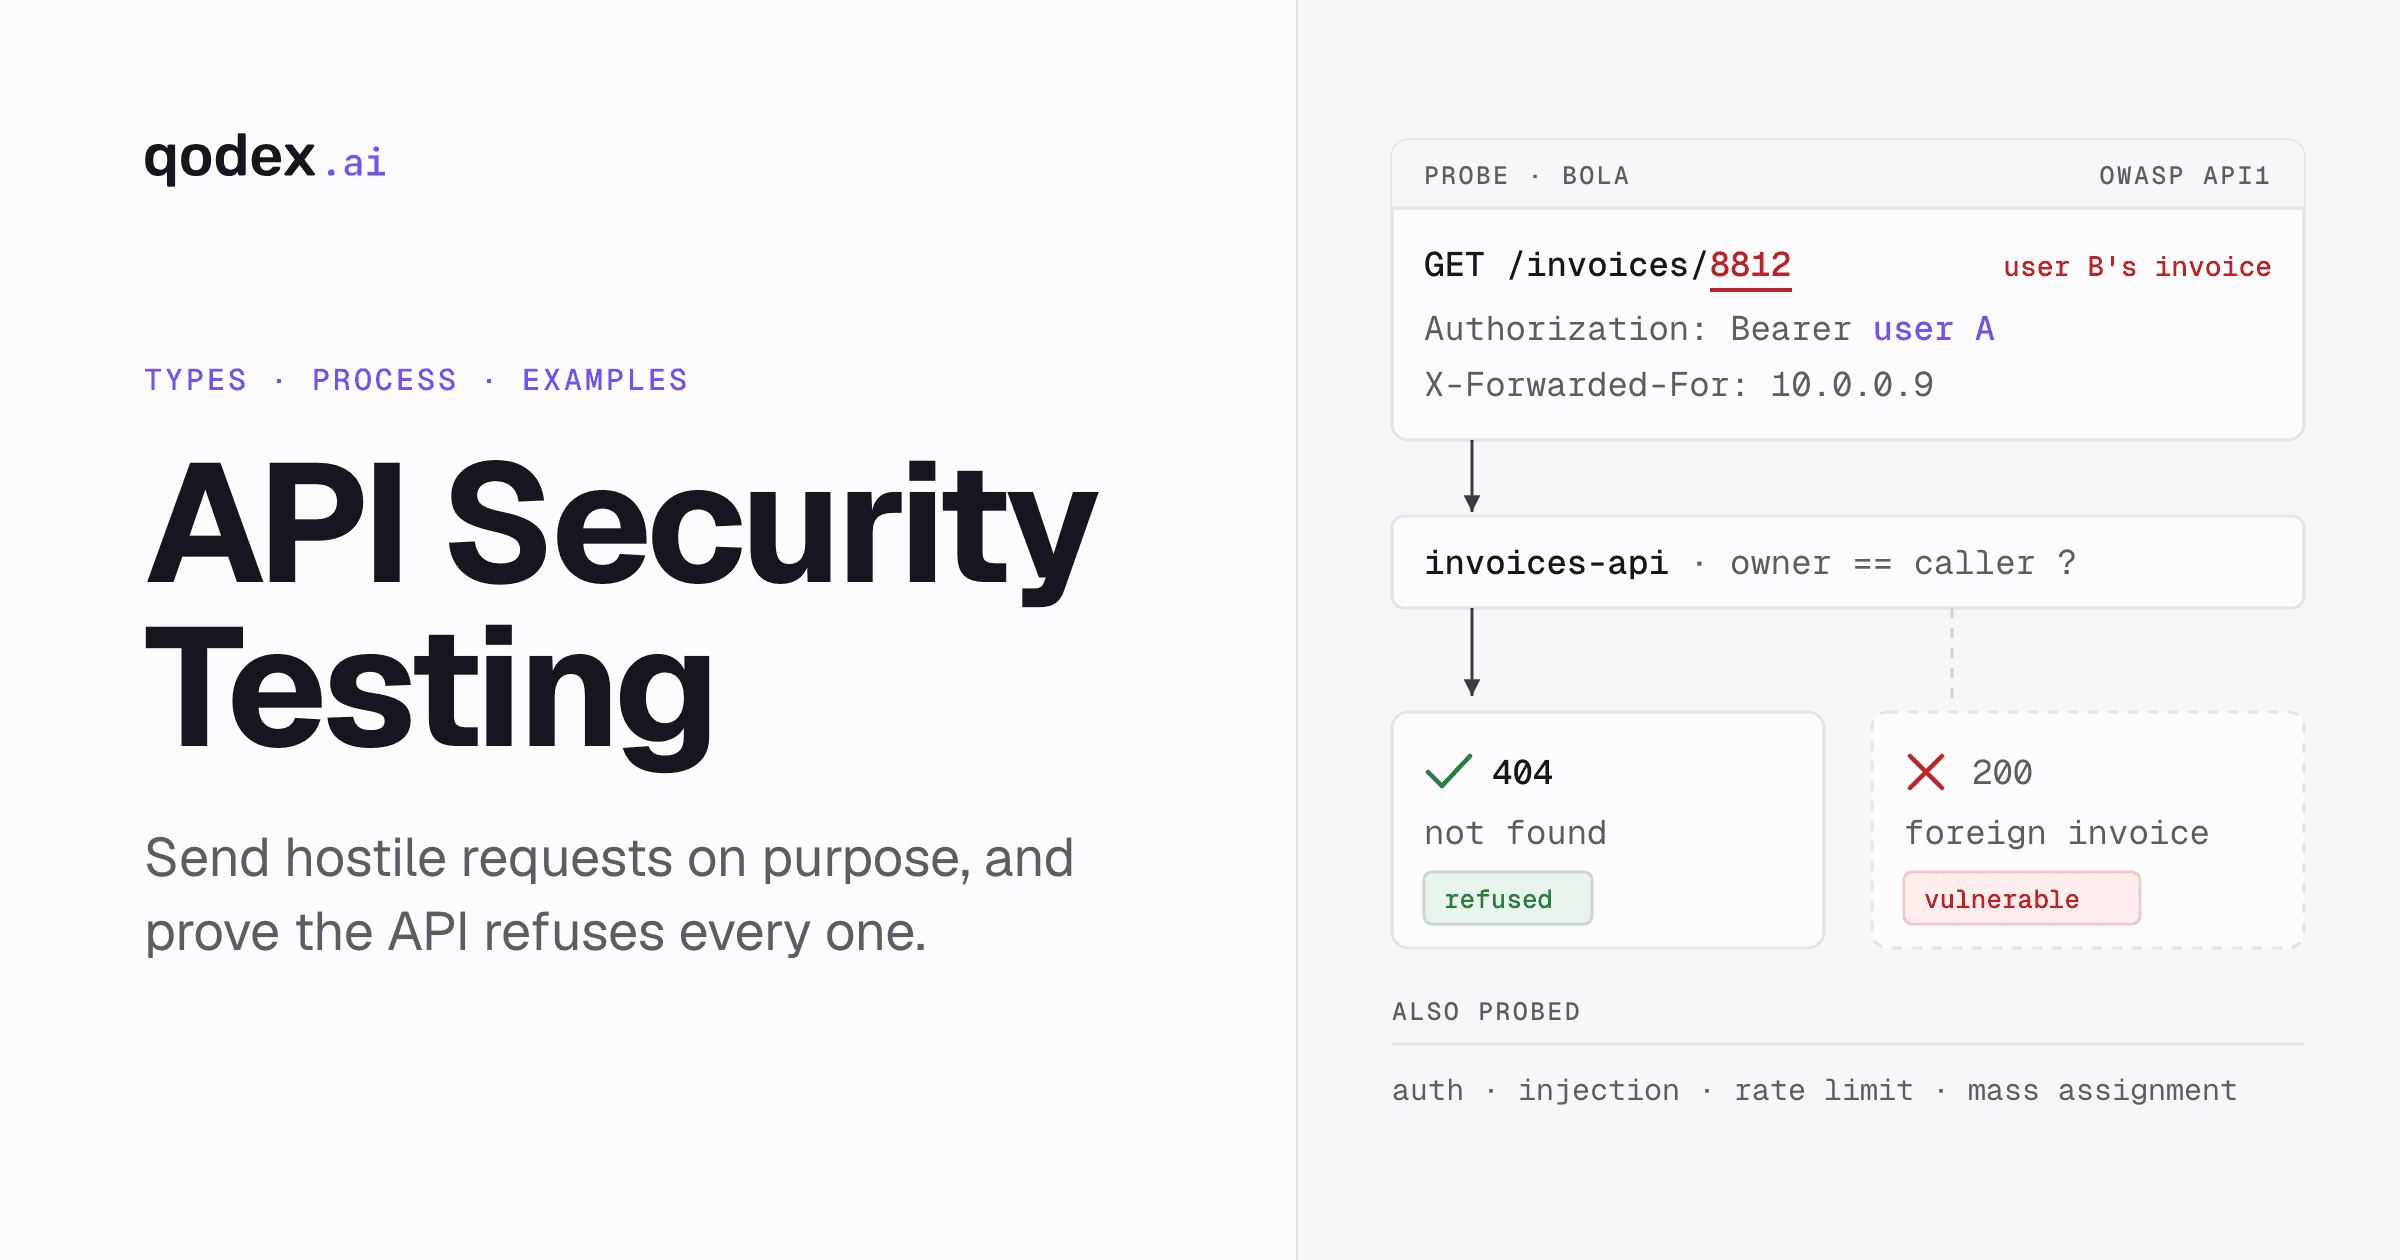
An API vulnerability scanner sends hostile and unexpected requests to a running API to find exploitable behavior. The best choice depends on your protocol, authentication flow, test environment, and evidence needs. Qodex is strongest when you want authenticated attack chains against every pull request preview. ZAP is the free baseline, Burp Suite suits hands-on testers, and StackHawk fits teams that want multi-user DAST in CI/CD.
This page compares twelve of them on one template. Each entry covers what the tool sends, what it needs to learn your API, whether it can hold two identities, what a finding looks like, how it runs unattended, and what the vendor charges. Every price is the vendor's own published figure, read 16 September 2026, or the words contact vendor where none is published. No tool was run for this page, so nothing here is a benchmark result. The protocol for running one is below.
Quick comparison: 12 API vulnerability scanners
The table is a shortlist filter, not a ranking. Read it by column: pick the column that decides your purchase, then read only the entries that survive it. If you need two identities against a real tenant boundary, read the auth column first. If the scanner has to run unattended on a branch, read the CI/CD column first. Price is last on purpose, because a tool that fails the first two columns is not cheap at any number.
| Tool | Test type and API inputs | Auth and multi-user tests | Evidence and retest | CI/CD and deployment | Published price | Best for |
|---|---|---|---|---|---|---|
| Qodex | Attack chains against a running preview, built from flows it has already run | Two real accounts in two organizations you control | The executed request, response, and step, with inverted assertions | Runs on every pull request, on demand, on a schedule, from CI or a webhook. Hosted | Individual $0, Startup from $1,299 per project monthly | Authenticated chains on every pull request |
| StackHawk | DAST driven by an OpenAPI, GraphQL, or SOAP definition | Multiple profiles, cross-profile BOLA and BFLA plugins | Rescan to verify the fix held | Built for pipeline runs. Scanner you run, results in the platform | Wingman $10 per user monthly, 50 scans per user; Scale on request | Multi-user DAST inside CI |
| OWASP ZAP | Active scan from an OpenAPI, SOAP, or GraphQL definition | Operator's own work through scripts and contexts | Alerts, rerun by script | Docker image with documented exit codes. Self-hosted | Free, open source | A free CI baseline |
| Burp Suite | Manual proxy plus automated scanner | Manual setup; multi-user behavior not verified | Whatever the tester can demonstrate | Driven by a person. Desktop | Community free, Professional $499 | Hands-on testers |
| 42Crunch | Contract audit plus vulnerability and identity scan from OpenAPI | Identity scan is a named product | Audit score and scan findings against the contract | CI/CD integration listed under Enterprise. Hosted | 14-day trial, Individual $9 monthly for 1,000 tokens | Teams with accurate OpenAPI contracts |
| Escape | Business-logic-aware DAST for REST and GraphQL | Vendor describes authenticated business-logic testing | Vendor claims exploit proof and a retest | Not published | Contact vendor | GraphQL-heavy estates |
| APIsec | Continuous validation with business-logic attacks | Vendor lists BOLA and RBAC tests | Vendor claims exploit proof | Hosted, priced per 100 endpoints | Free $0; Standard $690 monthly per 100 endpoints; Pro $2,750 monthly per 100 endpoints | Endpoint-priced continuous validation |
| Nuclei | YAML templates fired at HTTP and other protocols | Template author's responsibility | The matched template | Single binary, documented CI integrations. Self-hosted | Free, open source, MIT | Targeted checks you write yourself |
| Schemathesis | Property-based tests generated from a schema | Credentials passed to the run, not an authorization review | A minimal curl reproducer per finding | CLI, pytest, and GitHub Actions. Self-hosted | Free, open source | Schema conformance and crash hunting |
| RESTler | Stateful REST fuzzing from an OpenAPI definition | Token refresh script supplied by the operator | Bug buckets with a replay log | Command line in four modes. Self-hosted | Free, open source, MIT | Deep stateful fuzzing of REST |
| Akto | Traffic-learned inventory plus business-logic tests | Vendor lists authentication test categories | Findings tied to the learned traffic pattern | Self-hostable core, MIT | Free, open source core; commercial tiers on request | Inventory first, testing second |
| Invicti | API discovery plus stateful DAST | Tokens, cookies, and OAuth2, with BOLA and BFLA tests | Proof-based validation, suppression, and deduplication | Platform integrations. Hosted or on-premises | Contact vendor, 7-day trial advertised | Large estates with shadow APIs |
What an API vulnerability scanner actually tests
A scanner in this category talks to a running API. It builds requests a well-behaved client would never send, watches what comes back, and reports the responses that suggest the API will do something it should not. That is dynamic testing, usually shortened to DAST, and it means the API has to be up. A scanner cannot tell you what your code says, only what your service did when something pushed on it.
Several adjacent controls get sold in the same sentence and do a different job. Spec linters check that an OpenAPI file is well formed and does not describe an insecure design. Static analysis reads source. Software composition analysis matches dependencies against known vulnerable versions. Posture tools inventory what you expose. Runtime protection blocks requests in production. Network vulnerability managers such as Nessus, Qualys, Rapid7, OpenVAS and Nmap scan hosts and services, and container and dependency scanners such as Trivy and OSV-Scanner scan images and lockfiles. Specialist testers such as sqlmap go deep on one class. All are useful and none is an API vulnerability scanner. If you want the wider category rather than this subset, the API security testing tools roundup covers it.
The risks worth finding are the ones in the OWASP API Security Top 10, whose current edition is the 2023 one. Five of the ten are authorization and authentication risks: broken object level authorization, broken authentication, broken object property level authorization, broken function level authorization, and unrestricted access to sensitive business flows. The other five are unrestricted resource consumption, server side request forgery, security misconfiguration, improper inventory management, and unsafe consumption of APIs. A tool that lists all ten on a feature grid has not proved it finds all ten on your API. The OWASP API Security Top 10 guide shows what each looks like in a real request, and API security testing covers the method around the tool.
How to compare API vulnerability scanners
No tool here was run for this comparison. What follows is the protocol you would run to settle it for your own stack, written so the result is comparable across tools rather than a set of impressions. It will tell you more than any vendor grid, including this one.
Start with one disposable API you control, with an OpenAPI file that matches what it serves. Stand up three identities: two peers in separate tenants and one admin. Load cross-tenant data, so account A owns records account B must never read. Then plant known flaws and write down where you put them. A broken object level authorization on a record fetch, where the object id comes from the path instead of the session. A broken function level authorization on an admin route that only checks a token exists. One injection sink. One server-side request forgery in a callback URL field. One schema flaw, a field the server accepts but the spec forbids. Finally plant a control: a route that looks suspicious and is correctly guarded. A tool that reports the control is telling you about its false-positive behavior.
Run every tool against that target and record the same things. Setup time from install to first request. How you authenticated it, and whether it stayed authenticated. How much of the API it reached, in routes touched, not requests sent. Which planted flaws it found, which findings were wrong, which flaws it missed. Whether it wrote or deleted data. Wall-clock duration. The exit code in CI. Whether a suppression survives the next run. Whether a fix can be retested without a full rescan. And whether you could reproduce each finding from the tool's output alone.
That last one separates the list from the shortlist. A finding you cannot reproduce from the evidence pack is a ticket your engineers argue with rather than fix. Keep the target, the planted flaws and the results in version control, because the comparison is worth rerunning when a tool ships a major version.
The 12 best API vulnerability scanner tools
1. Qodex
Qodex runs authenticated security chains against your preview. It starts from the authenticated flows it has already run, not a cold crawl. Everything it reports was executed against your preview, so a finding is a path that worked, not a score that might.
For multi-user testing it uses an owner and a member, in two organizations you control, so IDOR and privilege escalation are tested the way they happen. Each finding carries the request, the response, and the step that let it through. A pass means the attack was blocked: assertions are inverted on purpose, so relaxing one cannot turn a failure green and the number you see cannot be gamed. A fixed chain stays fixed on the next run, or the run goes red again.
It runs on every pull request against its preview, on demand, on a schedule, from CI or a webhook. Nothing to install and no runner in your pipeline. Individual is $0 with up to 25 test scenarios and 100 test runs per month and core OWASP-aligned security probes. Startup is from $1,299 per project per month and adds the full OWASP security suite. Best for teams who want the authorization boundary tested before the merge rather than once a quarter. Details: Qodex security testing.
2. StackHawk
StackHawk is DAST built for a pipeline rather than a security analyst's desktop. It takes an OpenAPI, GraphQL or SOAP definition and drives an active scan from it, so coverage tracks the spec you already publish.
Its multi-user work is why it is on this list. Give it more than one authentication profile and the cross-profile plugins attempt to read resources discovered by one profile using another profile's credentials, which is the BOLA test written properly. Broken function level authorization runs the same way. StackHawk's documentation is blunt about the prerequisites: at least two accounts and representative test data, pointed at a staging environment.
A rescan is the confirmation step: the pricing page describes fixing a vulnerability and then rescanning to verify the fix held. You run the scanner yourself and read the results in the StackHawk platform. Wingman is $10 per user per month with unlimited apps and 50 scans per user per month, on a 14-day free trial; the Scale plan is quote-based. Best for teams who already have an OpenAPI file and want authorization coverage inside CI.
3. OWASP ZAP
ZAP is the free baseline every other tool here gets measured against, and the API scan script is the part that matters. It is tuned for scanning APIs defined by OpenAPI, SOAP or GraphQL, from a local file or a URL. It imports the definition, runs an active scan, and reports.
The CI story is better than its reputation suggests, because the exit codes are documented. The script exits 0 for success, 1 when there is at least one FAIL, 2 when there is at least one WARN and no FAILs, and 3 for any other failure. By default every alert is a warning, and a configuration file overrides that, which is how ZAP becomes a gate that fails builds only on what you decided matters.
Authentication and alert tuning are your work: the operator supplies the session, and a second identity is something you script. Evidence is the alert the scan reports. Deployment is the ZAP Docker image, self-hosted, free. Best for a free CI baseline.
4. Burp Suite
Burp is a manual proxy with an automated scanner attached, and the manual half is the point. For API work, Burp Scanner parses OpenAPI definitions, SOAP WSDLs, Postman Collections exported in v2.1.0 format, and GraphQL APIs with introspection enabled. The OpenAPI requirements are strict in a useful way: JSON or YAML, no external references, and server URLs Burp can reach.
Burp is a manual proxy plus an automated scanner. Its manual depth depends on the tester's skill.
Community is free. Professional is listed at $499, alongside a free trial, on the Burp Suite Professional page, read 16 September 2026. Best for hands-on testers, and for the moment a scanner produces something odd and you take the request apart by hand.
5. 42Crunch
42Crunch works from the contract outward: an API audit that scores the OpenAPI definition itself, an API scan that tests the running API against that definition, and an identity scan. The audit catches a design flaw before anything is deployed, which is a different place to catch it.
The prerequisite is the thing that makes it useful: your OpenAPI file has to be accurate, because a drifted contract produces an audit of a service you are not running. The three products to ask about by name are the API audit, the API scan and the identity scan, plus the security quality gate.
The trial runs for 14 days, and Individual starts at $9 per month for 1,000 security tokens. CI/CD integration is listed under Enterprise, the line to check before buying a lower tier. Best for teams whose OpenAPI contracts are already the source of truth.
6. Escape
Escape sells business-logic-aware DAST for REST and GraphQL. Its own page pairs AI-powered authentication with business-logic testing, and describes proof of what is exploitable followed by a retest. Those are vendor claims, with no independent run behind them here.
The pricing page published no dollar figure when read on 15 September 2026, so the entry is contact vendor. Best for GraphQL-heavy estates where a generic OpenAPI-driven scanner runs out of things to say.
7. APIsec
APIsec runs continuous validation rather than scheduled scans, and its published feature list leads with business-logic attacks: broken object level authorization and role-based access control tests. Its framing is what an attacker can actually exploit rather than a finding count. Authentication support is listed on the custom Bug Bounty tier.
The free tier covers public API testing with basic test simulations, a cheap way to see the output format first. Private and on-premises testing is custom work.
Pricing is per 100 endpoints, and the figures are published. Read 16 September 2026: Free at $0 forever, Standard at $690 a month per 100 endpoints or $8,275 a year, and Pro at $2,750 a month per 100 endpoints or $33,075 a year. Endpoint-based pricing rewards an accurate inventory, so count before you quote. Best for teams that know their endpoint count and want validation priced against it.
8. Nuclei
Nuclei is an MIT-licensed scanner driven by YAML templates. Its repository lists support for TCP, DNS, HTTP, SSL, WHOIS, JavaScript and code, templates contributed by thousands of security professionals, and CI/CD integration for detection and regression testing. Read 16 September 2026.
Nuclei's coverage and accuracy are both properties of the templates you run, not of the engine. The repository's language about simulating real-world steps "leading to zero false positives" is the project's own wording, not an independent measurement, and a badly written template produces noise like any other check.
For API work it is a precision instrument: you know a class of flaw exists in your stack, you write a template, and every service gets checked for it on every build. An authorization boundary and a second identity are things the template author builds, not things the engine knows about. Free and self-hosted. Best for targeted checks you write and own yourself.
9. Schemathesis
Schemathesis generates property-based tests from your schema and throws them at the running API. Supported specifications are OpenAPI 2.0, 3.0, 3.1 and 3.2, and GraphQL from June 2018 on. Stateful testing follows OpenAPI links, infers relationships where they are not declared, and carries real identifiers between operations.
Its best property is the evidence. Every finding ships with a minimal curl reproducer, so a bug report is a command an engineer pastes rather than a screenshot they interpret. Its own page lists CLI, pytest and GitHub Actions, plus Allure, JUnit XML and HAR output. Read 16 September 2026.
It finds conformance and crash behavior: responses that contradict the schema, and sequences that break state. It takes credentials, but it is not an authorization review; nothing in it knows account B should not read account A's invoice. Free, self-hosted. Best for teams who want schema truth enforced continuously.
10. RESTler
RESTler is Microsoft Research's stateful REST fuzzer, MIT-licensed. Given an OpenAPI definition it analyzes the whole specification, infers producer-consumer dependencies between request types, and generates sequences where one call's output feeds the next. That is how it gets past the layer where most fuzzers stall.
It runs in four modes. Compile builds the grammar from the spec. Test executes every endpoint and method once to debug the setup and compute spec coverage, effectively a smoke test. Fuzz-lean runs every endpoint and method once with a default set of checkers. Fuzz is the breadth-first bug hunt, and the documentation carries an explicit warning: this mode is more aggressive and may create outages in a poorly implemented service, including resource leaks, performance degradation, and backend corruption. Point it at production and you own the result.
Findings are triaged into bug buckets, each with a replay log that reproduces the bug. Free, self-hosted, command line. Best for deep stateful fuzzing of a REST API you can afford to break.
11. Akto
Akto's open-source core is MIT-licensed and self-hostable. Its strength is the order it works in: build an API inventory by reading real traffic from sources such as Burp Suite, AWS, Postman, GCP and gateways, then test what it found. That covers the OWASP Top 10 and HackerOne Top 10 categories including BOLA, authentication, SSRF and XSS, and the vendor argues for fewer false positives because the engine reads traffic patterns before it tests.
Inventory-first is the right sequence when nobody knows how many APIs are in production, because a scanner pointed at a spec finds nothing about a service that has no spec.
One thing to check before you buy. The project's public identity as of 15 September 2026 describes itself as an AI security platform for securing AI agents, MCP servers, LLMs and generative AI apps. The API testing core is still in the repository, but confirm the commercial product's current API scope with the vendor. Open-source core is free; commercial tiers are quote-based. Best for estates where discovery is the bottleneck.
12. Invicti
Invicti extends a long-standing web DAST product into API security. Its published capability list covers API discovery that reconstructs specs for undocumented services, and stateful scanning that infers parameter relationships to reach business-logic flaws. Authentication uses tokens, cookies and OAuth2, and BOLA, BFLA and unauthenticated-access tests are named directly.
Its differentiator is what the vendor calls proof-based validation, with suppression and deduplication on top, under the platform's "zero noise" banner. That phrase is marketing wording rather than a measured false-positive rate, so ask for the proof format in an evaluation and judge it against the reproduce-from-output test above.
Deployment is the platform, hosted or on-premises. No public price is exposed on the API security product page, so the entry is contact vendor. A 7-day free trial is advertised on that page, read 16 September 2026. Best for large estates whose first problem is shadow APIs nobody documented and whose second is triage across hundreds of services.
How to choose by API, authentication, and workflow
Start with the protocol, because it eliminates fastest. A REST API with a maintained OpenAPI file opens every door here. For GraphQL, the tools whose own documentation names it are ZAP, Burp through introspection, StackHawk, Escape and Schemathesis. For SOAP, they are ZAP, Burp through WSDL, and StackHawk. All read 16 September 2026. For gRPC, check each vendor before you shortlist, and plan on writing tests rather than buying a scanner.
Then ask what the scanner logs in as. Most buyers answer this last and should answer it first. If the flaws that would hurt you are authorization flaws, and for most SaaS APIs they are, a tool that holds one session at a time cannot find them. It never has both identities in play, so it cannot tell you whether customer B can read customer A's data. Qodex and StackHawk document explicit multi-user testing. APIsec and Invicti name authorization tests, but the reviewed sources do not establish two-identity behavior. ZAP, Burp and Nuclei leave the second identity to you to script. Schemathesis and RESTler are not trying to.
Then ask where it runs and who triggers it. A scanner a person has to start gets run before audits and forgotten between them. A scanner wired to a pull request runs on the change that introduced the flaw, while the author still remembers why. Check the deployment model too: hosted tools need to reach your environment, and self-hosted tools need somewhere to live.
Last, decide what environment you will point it at. StackHawk's documentation asks for a staging or test environment, and RESTler attaches an outage warning to its aggressive mode. A preview environment per branch is cleanest: disposable, real code, and nobody pages you when a fuzzer fills a table.
How to judge false positives and test evidence
False-positive rates in vendor material are marketing until someone runs a control. The planted control above is the cheap version of that test: a route that looks exploitable and is not. A tool that flags it has told you more than any datasheet will.
Evidence is the more useful signal, and it is easy to judge. Take one finding and reproduce it using nothing but the tool's output. Schemathesis sets the bar with a minimal curl reproducer per finding. RESTler ships a replay log per bug bucket. Qodex reports the executed request, the response, and the step that let it through. If reproducing a finding needs a login to the scanner, the evidence is a claim rather than a proof.
Then check the two properties that decide whether the tool survives its third month. Can you suppress a known-accepted finding so it stays suppressed, without suppressing the next real one that looks like it? And can you retest one fix without a full rescan? A scanner that gets both right becomes part of the regression suite, where a fixed flaw is rechecked on every change. A scanner that gets them wrong becomes a quarterly report.
Frequently Asked Questions
What is an API vulnerability scanner?
An API vulnerability scanner sends hostile and unexpected requests to a running API and reports the responses that suggest exploitable behavior. It tests the service as it runs, which is why it is dynamic testing. It is a different control from a spec linter, a source-code scanner, a dependency scanner, an inventory tool or a runtime blocker.
What is the best API vulnerability scanner?
There is no single answer, because these tools solve different halves of the problem. If the authorization boundary worries you and you want it checked before a merge, Qodex and StackHawk are designed for it. For a free baseline in CI today, ZAP. With a skilled tester driving, Burp Suite. If discovery is the bottleneck, Akto or Invicti.
What is the best free or open-source API vulnerability scanner?
ZAP is the best general-purpose free option: the API scan script takes an OpenAPI, SOAP or GraphQL definition and returns documented exit codes a pipeline can act on. Schemathesis suits schema conformance with reproducible failures, RESTler suits deep stateful REST fuzzing, and Nuclei suits a flaw class you will write the template for. All four are free and self-hosted.
Can an API scanner test authenticated endpoints?
Yes, and it should, because most of an API sits behind the login. The cost varies. Hosted platforms take credentials or a token refresh script as configuration. ZAP and Burp need authentication scripted by hand, and the session has to survive the scan. Check one thing in an evaluation: whether the scanner notices its session expiring halfway through, or quietly spends the rest of the run testing the login page.
Can scanners find BOLA, IDOR, and business-logic flaws?
Usually only with more than one identity. Broken object level authorization means account B reading account A's object, so a scanner holding one session has nothing to compare against. Tools that test it properly ask for at least two accounts, ideally in two tenants, then attempt the cross-read deliberately. StackHawk's cross-profile plugins and Qodex's two-account chains work that way. Business-logic flaws beyond authorization usually need scenarios that describe your domain.
How do API scanners reduce false positives?
Two mechanisms show up across these tools. Confidence scoring, which is a guess. And validation, where the tool attempts the exploit and reports only what worked. Qodex adds a third of its own, inverted assertions, where a pass means the attack was blocked, so relaxing a check cannot make a finding disappear. Vendor phrases such as "zero false positives" and "zero noise" are marketing wording, not measurements; run the planted control and find out.
What evidence should an API scanner provide?
Enough to reproduce the finding without the scanner: the exact request, the response that proves the impact, and the sequence of steps if more than one call was involved. A curl command is the gold standard, and Schemathesis ships one per finding. A replay log, as RESTler produces, is close behind. A severity score with a paragraph of generic advice is not evidence.
Is an API vulnerability scan the same as a penetration test?
No. A scan is automated and repeatable; a penetration test is a human exercising judgment your tooling does not have. No compliance framework accepts an automated scan in place of a pentest, and PCI DSS rules the claim out in its own text. The useful relationship is complementary: the scan covers the eleven months between pentests and regression-checks what the last one found. What is penetration testing covers the difference properly.
Should I scan production or staging?
Staging, or a per-branch preview environment. StackHawk's documentation asks for a staging or test environment, and RESTler attaches an explicit warning to its aggressive mode: fuzzing can cause outages, resource leaks and backend corruption in a service that handles it badly. A scanner may also write data, and cleaning test records out of a production database is nobody's good afternoon.
Does an API vulnerability scanner make an API FedRAMP compliant?
No. A scanner's output is one input to an authorization package, not the package. Buyers have to verify the deployment model, the reporting format, and the applicable control requirements separately, and those checks are about the environment and the process as much as the tool. No tool on this page should be described as FedRAMP-suitable on the strength of its scan output alone.
Shortlist and next step
Our recommendation, as an editorial one rather than a measured result. Qodex for authenticated attack chains on every pull request. StackHawk for multi-user DAST in CI against an OpenAPI file. ZAP for a free baseline running this week. Burp Suite if a tester is driving. Pick two, run the protocol above against one disposable API for a day, and buy the one whose evidence your engineers act on.